
Advisory Database
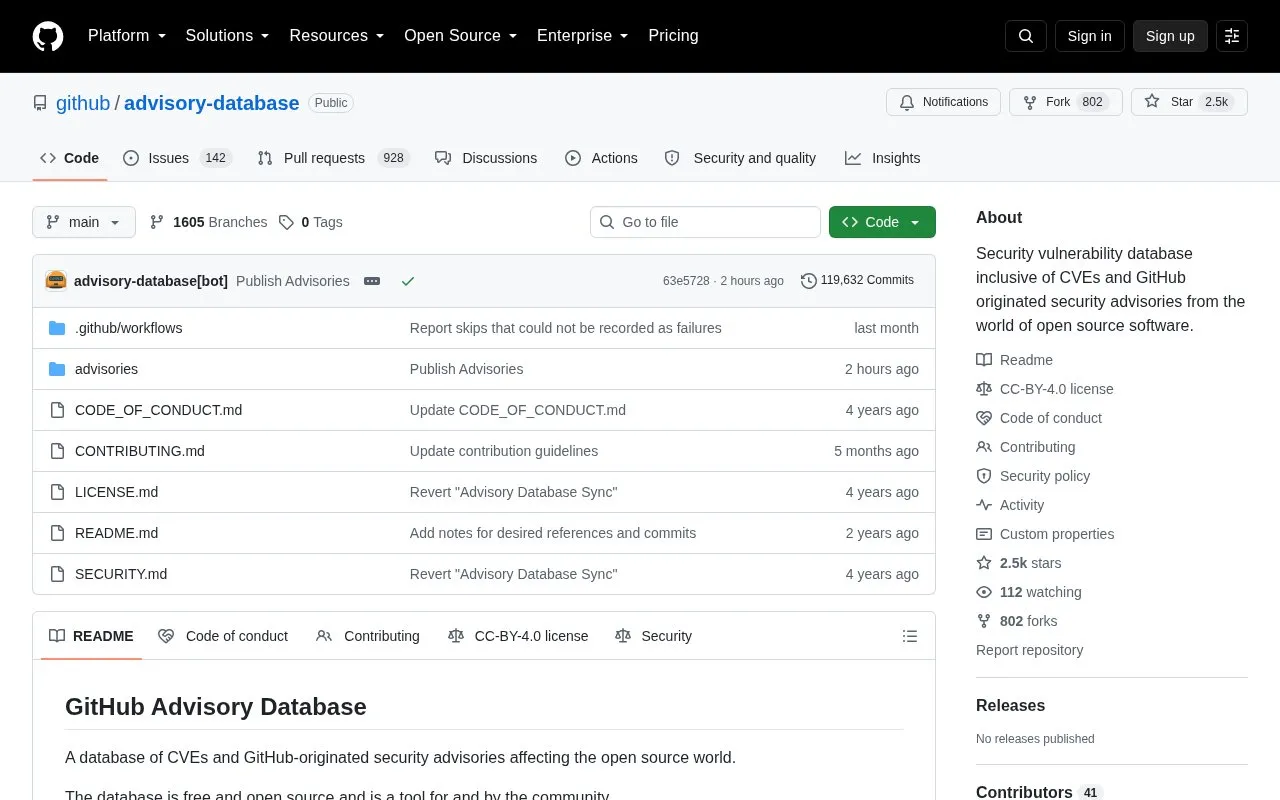
GitHub Advisory Database catalogs CVEs and GitHub-originated security advisories affecting open-source software.
About Advisory Database
Advisory Database catalogs CVEs and GitHub-originated security advisories affecting open-source software. Each advisory acknowledged by GitHub is stored as an individual file in Open Source Vulnerability (OSV) format, and content is drawn from GitHub reports, the National Vulnerability Database, several language-ecosystem databases, and community contributions.
Users can suggest improvements through github.com/advisories or by submitting a pull request against an advisory file, with changes reviewed by a curation team. Community contributions are not accepted for advisories outside the supported ecosystems.
Key features
- Stores each GitHub-acknowledged advisory as an individual OSV-formatted file
- Aggregates advisories from NVD, npm, FriendsOfPHP, Go, Python, Ruby, and RustSec
- Accepts improvement suggestions through the github.com/advisories form
- Accepts direct pull requests against advisory files
- Lists fix commits to help determine impact on build artifacts
- Covers Composer, npm, pip, Maven, NuGet, Go, Rust, and other registries
Best for: Developers and maintainers who work with packaged open-source dependencies and need vulnerability information.
Good for
- Described as free and open source
- Uses OSV format for machine interoperability
- Draws from multiple upstream vulnerability databases and community input
Watch out for
- Community contributions are not accepted outside supported ecosystems
- Pull request changes require review by the curation team
- References generally exclude secondary write-ups unless from the upstream source
Advisory Database at a glance
- Category
- Privacy & Security › Security Tools
- Type
- Open-source project
- Pricing
- Not confirmed. Check the site
- Open source
- Not stated
- Language
- English
- Last checked
- Oct 6, 2026 · Online when checked
- Listed
- Oct 5, 2026
Guides for Security Tools
Advisory Database alternatives
Tools and sites you could use instead, ranked by how closely they match.

GitDorker searches GitHub for exposed secrets using a collection of search patterns.

Agentic Radar scans agent workflows for security issues and helps developers review potential risks.
Open source
24 alternatives
unblob extracts files from complex binary blobs and firmware images, supporting security analysis of embedded software.

Instrument running software with Frida, a dynamic analysis toolkit for observing and reprogramming applications.

AndroGuard provides tools for reverse engineering and penetration testing Android applications.
Open source
24 alternatives
Find community-provided plugins for the Binary Ninja reverse engineering platform.
Open source
24 alternativesPopular in Security Tools
Well-known listings from the same topic.
Online Password Hash Crackonlinehashcrack.comOTP Authapps.apple.com/app/otp-auth/id659877384MD5 reverse lookupmd5.gromweb.comMozilla SSLssl-config.mozilla.orgchallenges.rechallenges.reGoPlus Locker V3gopluslabs.io


Advisory Database FAQ
How can I contribute corrections to an advisory?
Use Suggest improvements on github.com/advisories to open a pull request, or submit a pull request directly against the file following the contribution guidelines.
Which ecosystems accept community contributions?
Composer, Erlang, GitHub Actions, Go, Maven, npm, NuGet, pip, Pub, RubyGems, Rust, and Swift. Contributions outside these are not accepted.
Where does the database get advisories?
Security advisories reported on GitHub, the National Vulnerability Database, npm, FriendsOfPHP, Go, Python Packaging, Ruby, and RustSec databases, and community contributions.
Is something wrong or out of date?
Tell us and an editor will check it.
Own this website?
Claim this listing
Claim the listing and suggest updates yourself. An editor checks every claim first.