
Awesome Android Reverse Engineering
Browse Android reverse engineering training, tools, and learning resources in this curated repository.
About Awesome Android Reverse Engineering
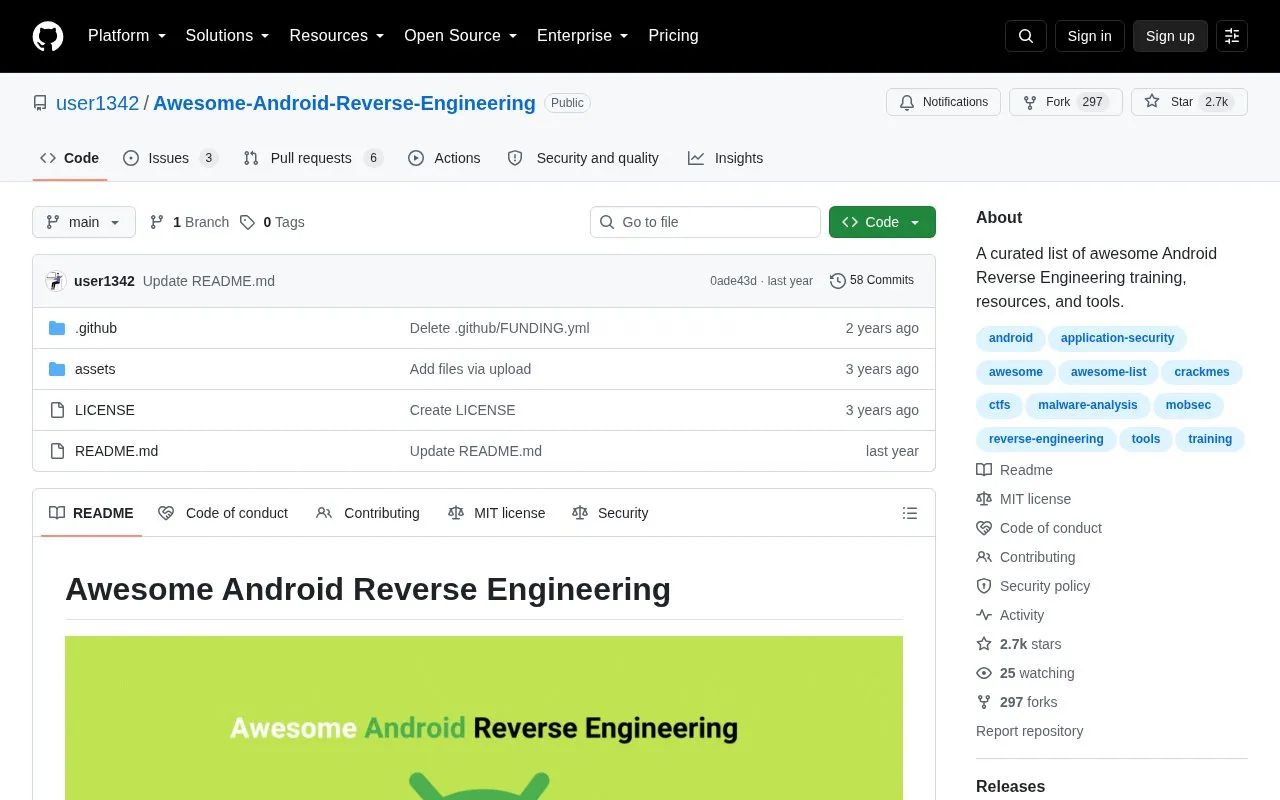
Awesome Android Reverse Engineering is a curated repository of Android reverse engineering training, resources, and tools. It organizes links into courses and materials, videos, books, static and dynamic analysis tools, de-obfuscation, networking and runtime instrumentation tools, plus sections for malware analysis, case studies, CTFs, obfuscation, firmware and kernel analysis, and cloud API reversing. Users find items by keyword search or the contents menu, with a star marker used to note up-to-date resources.
Key features
- Lists training courses and materials for Android reverse engineering
- Collects videos on basics, malware analysis, and Frida use
- Catalogs books on Android internals, ARM assembly, and security
- Lists static analysis tools such as QARK, MobSF, and AndroBugs
- Lists dynamic analysis, network traffic, and instrumentation tools
- Includes de-obfuscation tools such as simplify and deoptfuscator
Best for: It is useful for people who work in taking apart Android applications, systems, or components.
Good for
- Open-source repository covering training, books, videos, and tools
- Organizes resources into static, dynamic, networking, and instrumentation sections
- Uses star markers to identify resources noted as up-to-date
Awesome Android Reverse Engineering at a glance
- Category
- Privacy & Security › Security Tools
- Type
- Open-source project
- Pricing
- Not confirmed. Check the site
- Platforms
- Android
- Open source
- Yes · Source code
- Language
- English
- Last checked
- Oct 5, 2026 · Online when checked
- Listed
- Oct 5, 2026
Guides for Security Tools
Awesome Android Reverse Engineering alternatives
Tools and sites you could use instead, ranked by how closely they match.

Use reference sheets for reverse engineering, binary analysis, and assembly programming tools.
Open source
24 alternatives
Set up a Windows virtual machine for reverse engineering with FLARE-VM’s software installation scripts.
Open source
24 alternatives
Browse community-maintained materials and plugins for the Ghidra reverse engineering framework.

Browse plugins for x64dbg, a Windows debugger used for reverse engineering and malware analysis.

dnSpyEx continues the dnSpy project as a debugger and assembly editor for .NET.
Open source
24 alternatives
pyWhat identifies items such as email addresses and IPs from text or packet captures, according to its project description.
Open source
24 alternativesPopular in Security Tools
Well-known listings from the same topic.
Online Password Hash Crackonlinehashcrack.comOTP Authapps.apple.com/app/otp-auth/id659877384MD5 reverse lookupmd5.gromweb.comMozilla SSLssl-config.mozilla.orgchallenges.rechallenges.reGoPlus Locker V3gopluslabs.io


Awesome Android Reverse Engineering FAQ
How do I find resources in the list?
Press Ctrl + F to search by keyword, browse the Contents menu, or look for items marked with a star.
What does the star symbol mean?
It indicates resources noted as up-to-date.
Is something wrong or out of date?
Tell us and an editor will check it.
Own this website?
Claim this listing
Claim the listing and suggest updates yourself. An editor checks every claim first.