
Cli
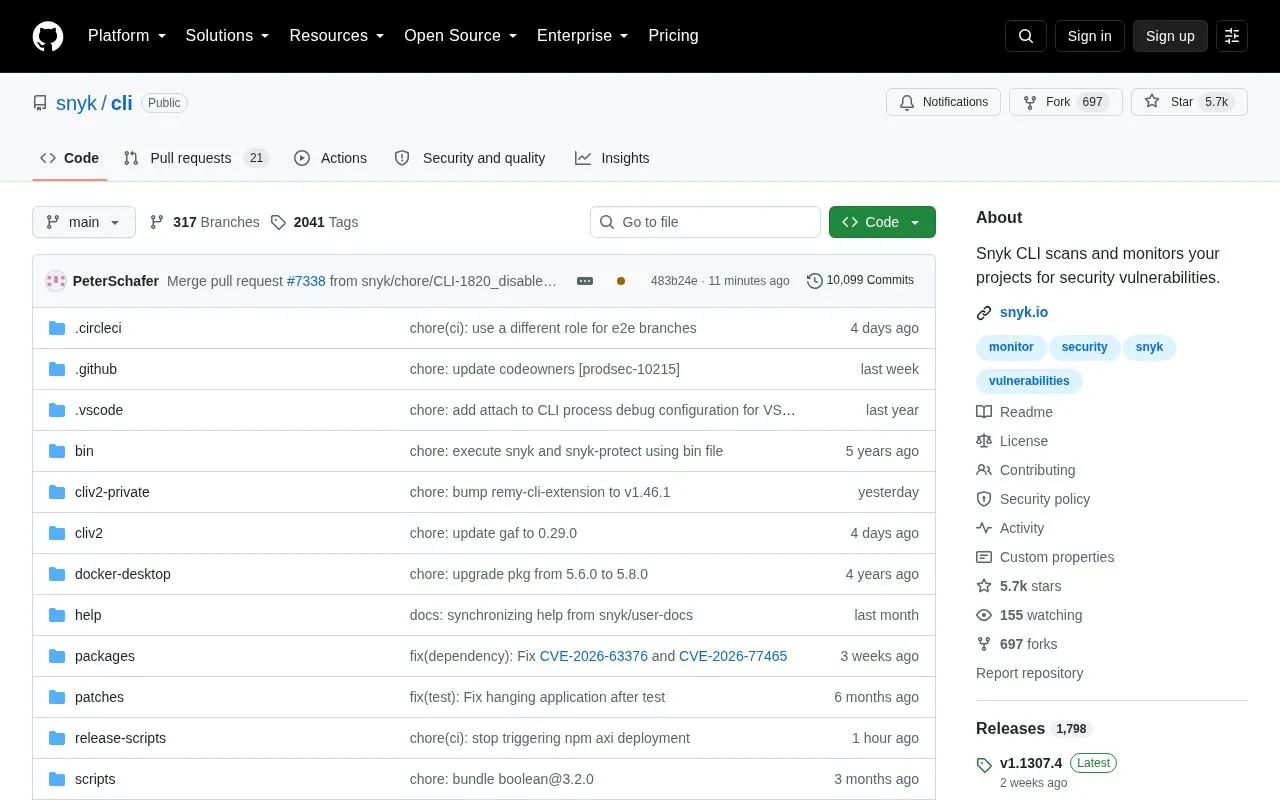
Snyk CLI scans and monitors software projects for security vulnerabilities.
About Cli
Snyk CLI scans software projects for security vulnerabilities from the development workflow. It covers open-source dependencies, application code, container images and Kubernetes applications, and Terraform and Kubernetes configurations.
It runs from the command line, in an IDE, or in a CI/CD pipeline. Use requires installing the CLI and authenticating the machine, and Open Source scanning requires the package manager, related tools in PATH, and building the project before testing, with limited exceptions.
Key features
- Scan open-source dependencies for vulnerabilities
- Scan application code for vulnerabilities
- Scan container images and Kubernetes applications
- Find insecure configurations in Terraform and Kubernetes code
- Run locally, in an IDE, or in CI/CD pipelines
- Test reports show severity, description link, entry path, and fix guidance
Best for: Developers who want to scan projects for vulnerabilities in local, IDE, or CI/CD workflows.
Good for
- Runs in command line, IDE, and CI/CD workflows
- Covers open source, code, containers, and IaC content types
- Test output includes severity, path, and fix guidance
Watch out for
- Requires installation and machine authentication before use
- Requires package manager and tools like Gradle or Maven in PATH for Open Source scanning
- Requires building Open Source projects before testing, with limited exceptions
Cli at a glance
- Website
- github.com/snyk/cli
- Category
- Privacy & Security › Security Tools
- Type
- Open-source project
- Pricing
- Not confirmed. Check the site
- Open source
- Not stated
- Language
- English
- Last checked
- Oct 5, 2026 · Online when checked
- Listed
- Oct 5, 2026
Guides for Security Tools
Cli alternatives
Tools and sites you could use instead, ranked by how closely they match.

Security and best-practice issues in container images can be checked with Dockle.
Open source
24 alternatives
Analyze software with Ghidra, a framework for reverse engineering compiled programs.
Open source
24 alternatives
Scan applications, APIs, networks, DNS, and cloud configurations for vulnerabilities using Nuclei.
Open source
24 alternatives
Nuclei scans for vulnerabilities using customizable templates written in YAML.

Agentic Radar scans agent workflows for security issues and helps developers review potential risks.
Open source
24 alternatives
Snyk helps software teams identify and manage security risks in code and dependencies while building AI-enabled applications.
Popular in Security Tools
Well-known listings from the same topic.
Online Password Hash Crackonlinehashcrack.comOTP Authapps.apple.com/app/otp-auth/id659877384MD5 reverse lookupmd5.gromweb.comMozilla SSLssl-config.mozilla.orgchallenges.rechallenges.reGoPlus Locker V3gopluslabs.io


Cli FAQ
Where can I run the Snyk CLI?
Locally from the command line, in an IDE, or in a CI/CD pipeline.
How do I test the installation?
Run snyk --help, or run snyk test ionic to test a public npm package.
What do I need before scanning Open Source projects?
Install the package manager, ensure tools such as Gradle or Maven are in PATH, and build the project, with limited exceptions.
Is something wrong or out of date?
Tell us and an editor will check it.
Own this website?
Claim this listing
Claim the listing and suggest updates yourself. An editor checks every claim first.