
Cynative
Cynative provides security agents that audit cloud, code, and runtime environments for exposure and privilege issues.
About Cynative
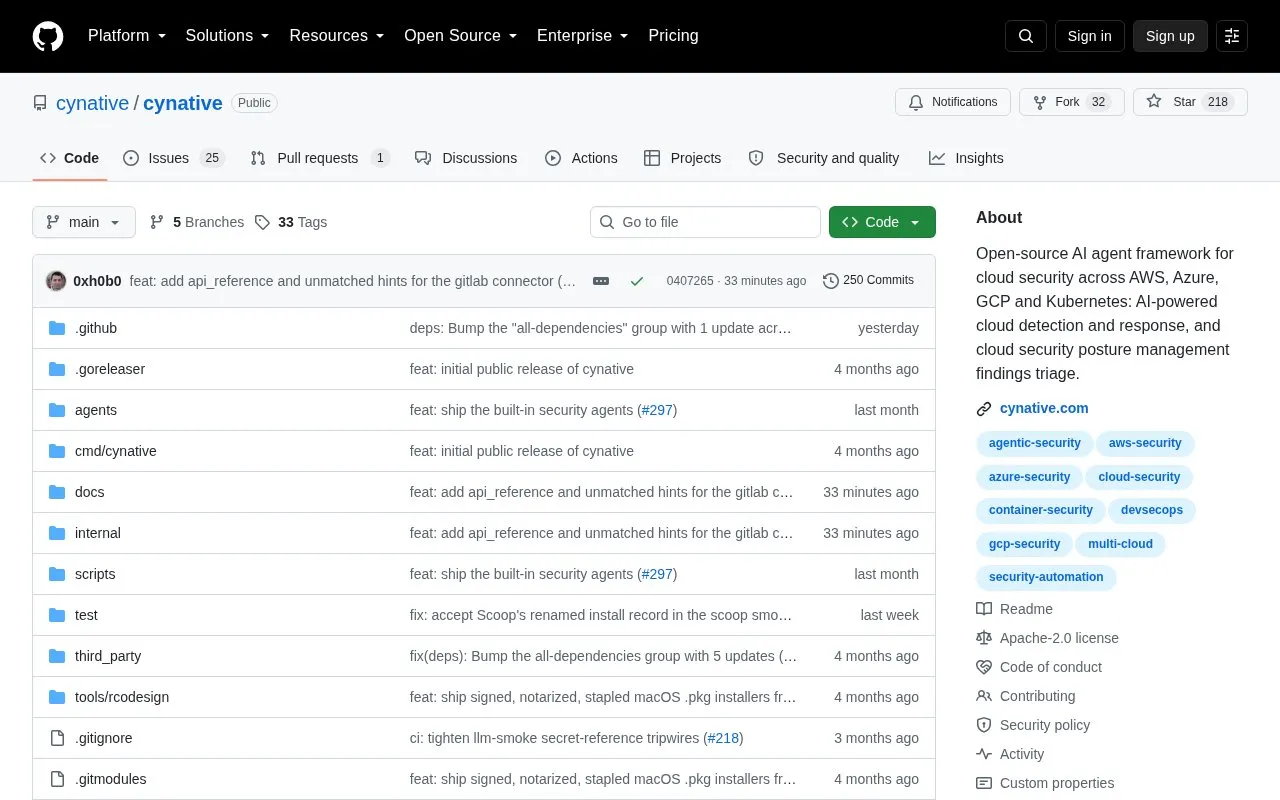
Cynative is an open-source framework for building and running security agents that check cloud, code and runtime environments for exposure and privilege issues. A user asks a question in natural language, and Cynative reasons across GitHub, GitLab, AWS, GCP, Azure and Kubernetes. It writes and runs code in an ephemeral sandbox to query APIs in parallel, then cross-checks each finding and traces it to its origin.
The framework ships with 45 built-in agents for AWS, GCP, Azure, GitHub and Kubernetes, covering topics such as privilege escalation, public exposure and supply chain. Users can also write their own agents as a single markdown file. The homepage describes the tool as read-only by construction, with each call gated and authorized before a credential is attached. Running it requires an LLM provider to be configured, and the quickstart shows an Anthropic API key set in the shell.
Key features
- 45 built-in agents for AWS, GCP, Azure, GitHub and Kubernetes
- Custom agents written as a single markdown file
- Natural-language questions spanning code, cloud and Kubernetes resources
- Read-only policy checked against IAM actions before a credential is attached
- Code execution in an ephemeral sandbox with no network or host access of its own
- Findings cross-checked and traced back to their origin
Best for: Security engineers and developers who want to audit cloud, code and Kubernetes environments using an AI model they configure themselves.
Good for
- Open source, with the source code and a LICENSE file in the repository
- Describes a read-only design in which every call is gated before credentials are attached
- Findings are cross-checked against each other before being reported
Watch out for
- Requires an LLM provider and its API key to be configured before use
Cynative at a glance
- Website
- github.com/cynative/cynative
- Category
- Privacy & Security › Security Tools
- Type
- Open-source project
- Pricing
- Not confirmed. Check the site
- Open source
- Yes · Source code
- Language
- English
- Last checked
- Oct 6, 2026 · Online when checked
- Listed
- Oct 5, 2026
Guides for Security Tools
Cynative alternatives
Tools and sites you could use instead, ranked by how closely they match.

BlackVault protects AI API credentials with rate limits, budget caps, model restrictions, and an emergency kill switch.
Open source
24 alternatives
ClawMoat helps guard AI agents against data leaks, unsafe tool use, and poisoned dependencies through an open-source firewall.
Open source
24 alternatives
Agentic Radar scans agent workflows for security issues and helps developers review potential risks.
Open source
24 alternatives
The action firewall for AI agents. Enforce policy and human approval before risky tool calls, shell commands, workflows, and production changes, with auditable evidence.

QWED verifies LLM outputs, tool calls, code, schemas, and agent state before production execution.
Open source
24 alternatives
Security and best-practice issues in container images can be checked with Dockle.
Open source
24 alternativesPopular in Security Tools
Well-known listings from the same topic.
Online Password Hash Crackonlinehashcrack.comOTP Authapps.apple.com/app/otp-auth/id659877384MD5 reverse lookupmd5.gromweb.comMozilla SSLssl-config.mozilla.orgchallenges.rechallenges.reGoPlus Locker V3gopluslabs.io


Cynative FAQ
How do I install Cynative?
The homepage lists a Homebrew install command, brew install cynative/tap/cynative. The repository also includes install.sh and install.ps1 scripts.
How do I create a custom agent?
Run cynative agents show with a built-in agent name to print its prompt, save a copy to ~/.cynative/agents under a new name, and edit the markdown file.
Does Cynative change resources in my cloud environment?
The homepage describes Cynative as read-only by construction, with every call gated and authorized before a credential is attached. It does not describe write actions.
Is something wrong or out of date?
Tell us and an editor will check it.
Own this website?
Claim this listing
Claim the listing and suggest updates yourself. An editor checks every claim first.