

ONYPHE scans IPs and URLs at internet scale for attack-surface discovery, management and cyber threat intelligence.
intelowlproject/IntelOwl
Coordinate threat intelligence processing and analysis at scale with IntelOwl, an open-source project.
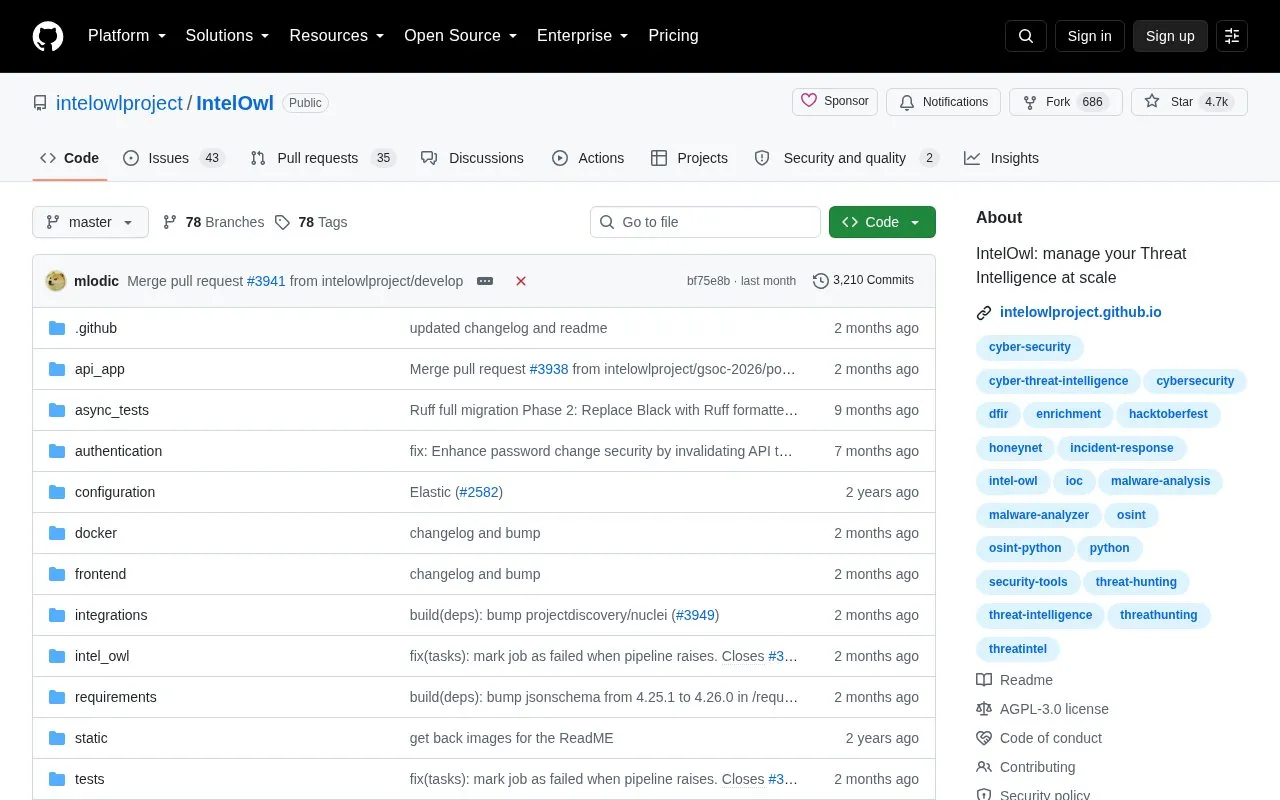
About intelowlproject/IntelOwl
IntelOwl is an Open Source solution for managing threat intelligence at scale. It enriches files and observables such as IP addresses, domains, URLs and hashes. Analyzers can pull data from outside sources like VirusTotal or AbuseIPDB, or produce results with internal tools like Yara or Oletools. Teams can review results in a built-in GUI and send data to platforms such as MISP or OpenCTI. It is aimed at teams that want to automate routine threat intelligence work and combine several analysis tools in one place.
Pricing is not clearly stated.
Key features
- Enrichment of files and observables such as IP, domain, URL and hash
- REST API written in Django and Python
- Built-in GUI with dashboards and visualizations
- Modular plugins for analyzers, connectors, pivots, visualizers, ingestors and playbooks
- Connectors that export results to MISP or OpenCTI
- Investigation support for registering findings and correlating information
Best for: Security teams that want to automate threat intelligence tasks, such as those usually done manually by SOC analysts.
Good for
- Released under the AGPL-3.0 license
intelowlproject/IntelOwl at a glance
- Category
- Privacy & Security › Security Research
- Type
- Open-source project
- Pricing
- Not confirmed. Check the site
- Details verified
- Oct 21, 2026 · Official source
- Open source
- Yes · Source code
- Language
- English
- Last checked
- Oct 5, 2026 · Online when checked
- Listed
- Oct 5, 2026
intelowlproject/IntelOwl alternatives
Tools and sites you could use instead, ranked by how closely they match.

Criminal IP provides IP reputation analysis, attack-surface monitoring, fraud detection and threat intelligence.

Cisco Talos provides threat intelligence and directs reputation or categorization inquiries to its support site.

Cisco Talos’ Intelligence Center provides IP and domain intelligence for threat detection.

Browse the APTnotes repository, which collects reports and reference material about APT activity.
Pick
24 alternatives
Analyze suspicious files or URLs in an online malware-analysis sandbox with ANY.RUN.
Popular in Security Research
Well-known listings from the same topic.
FortiGuardfortiguard.comgofoss.netgofoss.netCounter-OSINT guide for Russiansgithub.com/soxoj/counter-osint-guide-ruDigital Attack Mapdigitalattackmap.comGreyNoiseviz.greynoise.ioShodanshodan.io


Is something wrong or out of date?
Tell us and an editor will check it.
Own this website?
Claim this listing
Claim the listing and suggest updates yourself. An editor checks every claim first.