
Reversing Bits
Use reference sheets for reverse engineering, binary analysis, and assembly programming tools.
About Reversing Bits
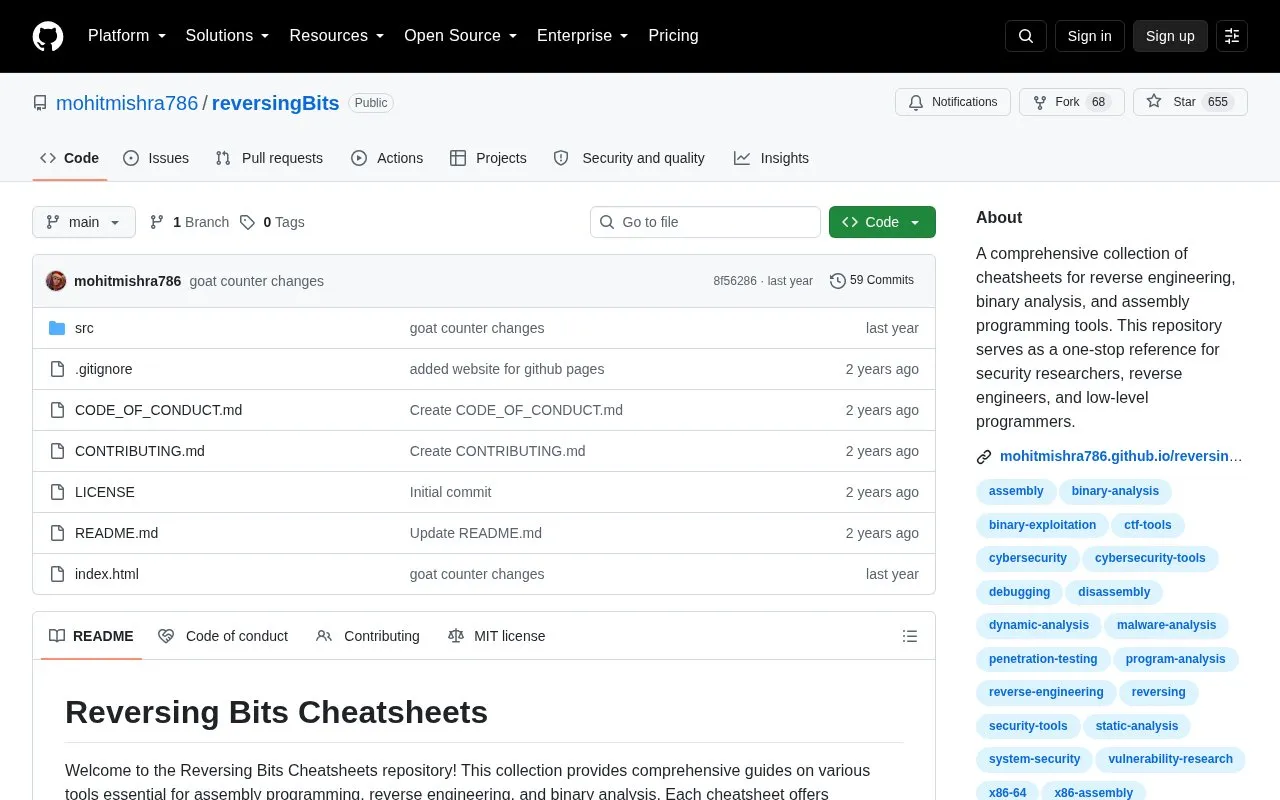
Reversing Bits is a GitHub repository of cheatsheets for reverse engineering, binary analysis, and assembly programming tools. Each cheatsheet covers a tool and includes installation instructions, usage examples, and advanced tips for different operating systems. The repository is organized into sections on assembly and basic analysis, debuggers and dynamic analysis, disassemblers and decompilers, binary analysis frameworks, and malware analysis and security.
The repository is a reference rather than software that runs analysis itself. It is licensed under the MIT License, and contributions are accepted through pull requests. The source does not state pricing details beyond the open-source license.
Key features
- Cheatsheets covering assemblers such as NASM and GAS
- Reference entries for debuggers including GDB, WinDbg, and Valgrind
- Sections on disassemblers and decompilers such as Ghidra, Radare2, and RetDec
- Binary analysis frameworks including Angr, Capstone, Frida, and Triton
- Malware analysis section listing YARA and Diaphora
- OS-specific installation instructions, usage examples, and advanced tips per tool
Best for: Security researchers, reverse engineers, and low-level programmers who want a single reference for a range of binary analysis tools.
Good for
- Open source under the MIT License
- Installation instructions are given for each operating system covered
- Covers a broad set of tools across assembly, debugging, disassembly, and analysis
Watch out for
- Some listed tools have stated scope limits, such as OllyDbg being a 32-bit debugger for Windows
Reversing Bits at a glance
- Category
- Privacy & Security › Security Tools
- Type
- Open-source project
- Pricing
- Not confirmed. Check the site
- Platforms
- Linux, Windows
- Open source
- Yes · Source code
- Language
- English
- Good for
- Researchers
- Last checked
- Oct 6, 2026 · Online when checked
- Listed
- Oct 5, 2026
Guides for Security Tools
Reversing Bits alternatives
Tools and sites you could use instead, ranked by how closely they match.

Set up a Windows virtual machine for reverse engineering with FLARE-VM’s software installation scripts.
Open source
24 alternatives
dnSpyEx continues the dnSpy project as a debugger and assembly editor for .NET.
Open source
24 alternatives
Browse Android reverse engineering training, tools, and learning resources in this curated repository.
Open source
24 alternatives
Browse plugins for x64dbg, a Windows debugger used for reverse engineering and malware analysis.

Malware investigation and reverse engineering are the focus of REMnux, a Linux toolkit that bundles analysis tools.

Browse community-maintained materials and plugins for the Ghidra reverse engineering framework.
Popular in Security Tools
Well-known listings from the same topic.
Online Password Hash Crackonlinehashcrack.comOTP Authapps.apple.com/app/otp-auth/id659877384MD5 reverse lookupmd5.gromweb.comMozilla SSLssl-config.mozilla.orgchallenges.rechallenges.reGoPlus Locker V3gopluslabs.io


Reversing Bits FAQ
Under what license is the repository released?
The repository is licensed under the MIT License, as described in its LICENSE file.
How can I contribute tools or improvements?
The repository asks contributors to fork it, make changes, and submit a pull request. The CONTRIBUTING.md file contains guidelines.
Is something wrong or out of date?
Tell us and an editor will check it.
Own this website?
Claim this listing
Claim the listing and suggest updates yourself. An editor checks every claim first.