
Shadowserver
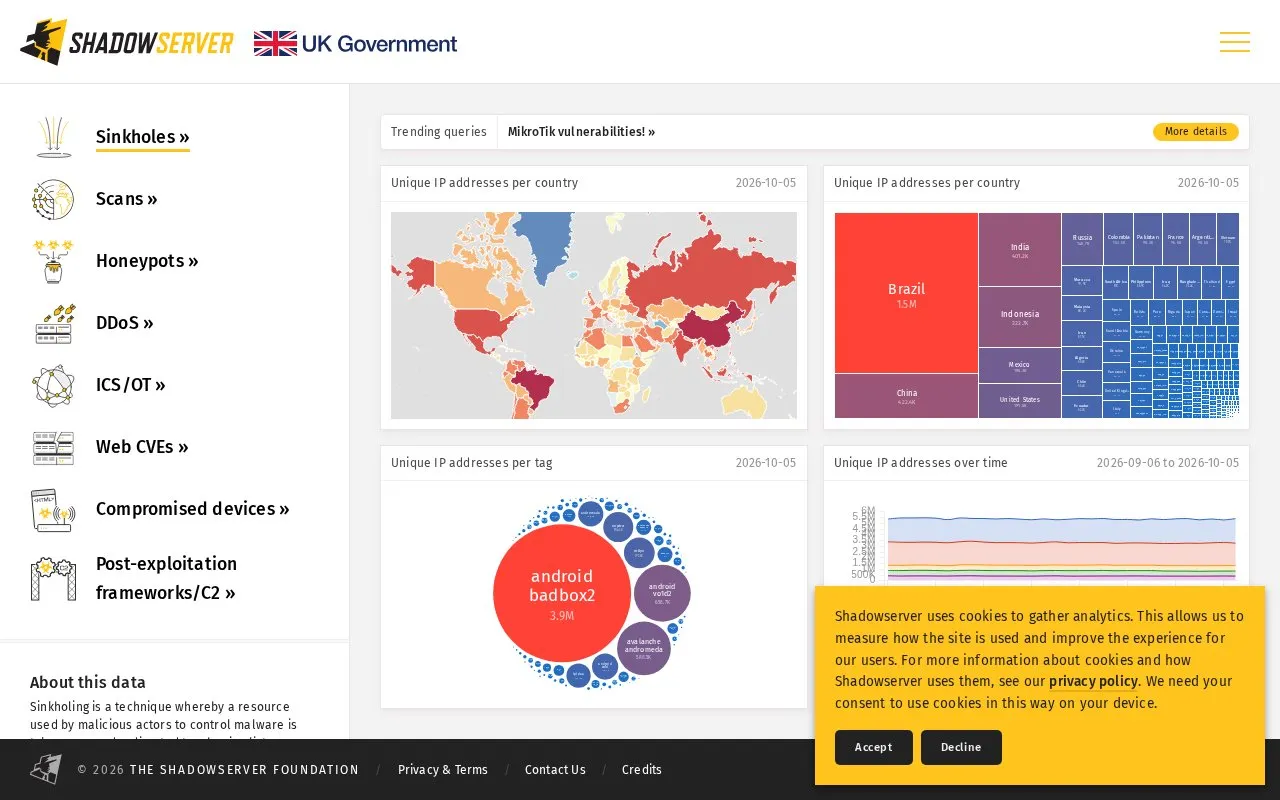
Shadowserver’s dashboard organizes reports on sinkholes, scans, honeypots, DDoS activity and compromised devices.
About Shadowserver
The Shadowserver Dashboard, published by The Shadowserver Foundation, presents reports grouped by threat area. The listed areas are sinkholes, scans, honeypots, DDoS activity, ICS/OT, web CVEs, compromised devices, and post-exploitation frameworks and command-and-control (C2) servers.
The homepage states that development was funded by the UK FCDO and that IoT device fingerprinting and honeypot attack statistics were co-financed by the EU Connecting Europe Facility (VARIoT project). It names partners that contribute data, including APNIC Community Feeds, Bitsight, CISPA, if-is.net, Kryptos Logic, SecurityScorecard, and Yokohama National University. The site uses analytics cookies only with user consent. The homepage does not describe report methods or coverage in detail.
Key features
- Sinkhole reports covering malicious domain and server traffic
- Scan reports organized in a single dashboard
- Honeypot attack statistics
- DDoS activity reports
- ICS/OT (industrial control systems and operational technology) reports
- Reports on compromised devices
- Groups several threat types, including sinkholes, honeypots and DDoS activity, in one dashboard
- Names the data partners that contribute to the dashboard
- Discloses public funding sources for development and specific statistics
Shadowserver at a glance
- Official website
- dashboard.shadowserver.org
- Category
- Privacy & Security › Security Research
- Type
- Institution
- Platforms
- Web
- Language
- English
- Last checked
- Oct 6, 2026 · Online when checked
- Listed
- Oct 5, 2026
Popular in Security Research
Well-known listings from the same topic.


Shadowserver FAQ
Who funded the Shadowserver Dashboard?
Where does the dashboard's data come from?
Tell us and an editor will check it.
Claim the listing and suggest updates yourself. An editor checks every claim first.