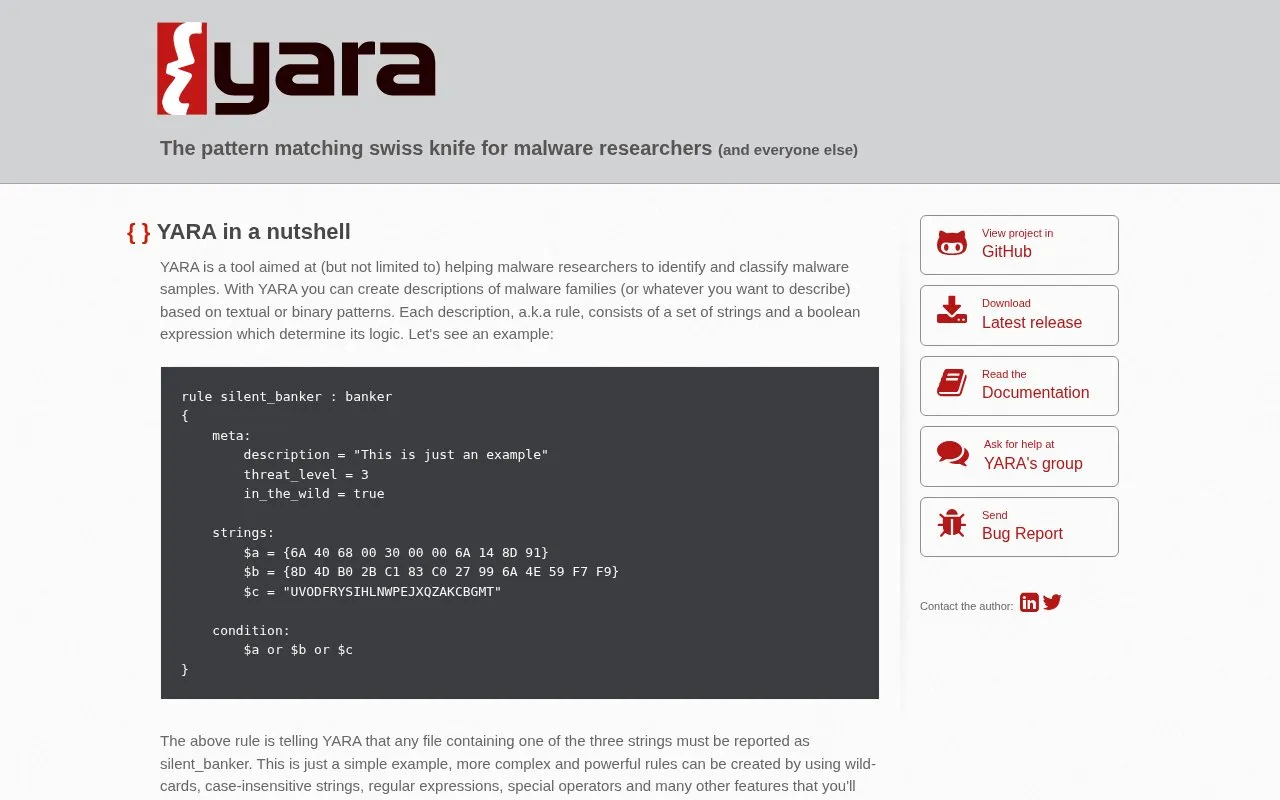
YARA is a pattern-matching tool used mainly by malware researchers to identify and classify malware samples. Each rule describes a malware family or other target using a set of textual or binary strings and a boolean condition that defines when the rule matches. The homepage says it is aimed at, but not limited to, malware research.
Rules can use wildcards, case-insensitive strings, regular expressions, and special operators. YARA runs on Windows, Linux, and Mac OS X and can be used from the command line or from Python scripts through the yara-python extension. The homepage points to a separate GitHub application, YARA-CI, for continuous testing of rules, and to yextend, an extension for scanning compressed files. The source does not state pricing beyond listing it as unknown.
Key features
Rules that match textual or binary patterns using boolean conditions
Support for wildcards, case-insensitive strings, and regular expressions
Command-line interface for scanning
Python scripting through the yara-python extension
Runs on Windows, Linux, and Mac OS X
YARA-CI, a GitHub application for continuous testing of stored rules
Best for: Malware researchers and analysts who write pattern-based rules to identify and classify malware samples.
Good for
Runs on Windows, Linux, and Mac OS X
Can be scripted from Python through yara-python
YARA-CI can test rules stored on GitHub for common mistakes and false positives
Watch out for
Scanning compressed files relies on the separate yextend extension, according to the homepage
Each rule consists of a set of strings and a boolean condition that determines its logic. The homepage gives an example in which a file matching any one of three strings is reported under the rule's name.
Can YARA rules be tested automatically?
The homepage describes YARA-CI, a GitHub application that provides continuous testing for rules stored there. It is intended to help identify common mistakes and false positives.
Can YARA scan compressed files?
The homepage says that scanning compressed files such as .zip and .tar can be done with yextend, an extension to YARA developed and open-sourced by Bayshore Networks.
Is something wrong or out of date?
Tell us and an editor will check it.
Own this website?
Claim the listing and suggest updates yourself. An editor checks every claim first.