
Sigma Prime audits smart contracts, zero-knowledge systems, blockchain infrastructure, and off-chain code, and publishes security research.
FailSafe
FailSafe builds continuous security testing systems that probe applications, APIs, infrastructure, and AI systems for exploitable issues.
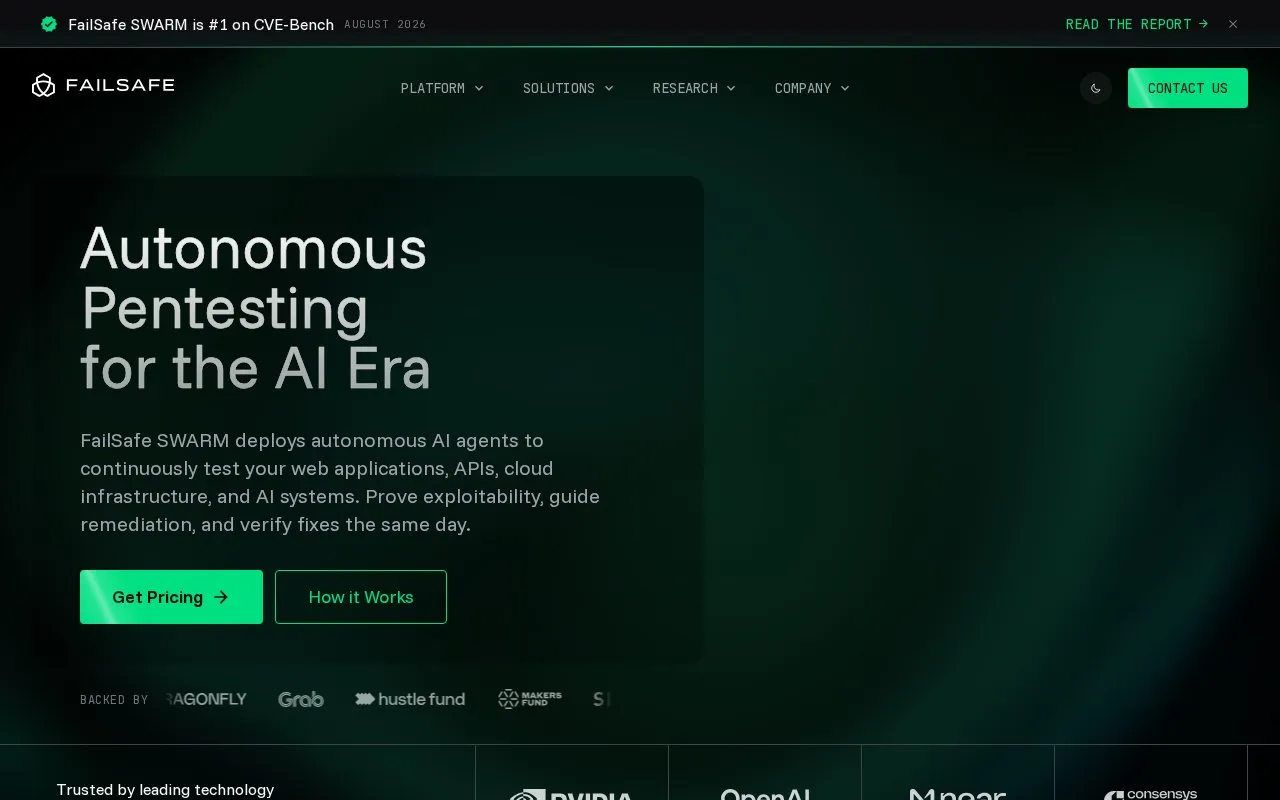
About FailSafe
FailSafe is a security company's website describing autonomous penetration testing and continuous offensive security systems. Its SWARM platform uses threat-model-driven AI agents to test web applications, APIs, cloud infrastructure, and AI systems. According to the site, SWARM validates suspected vulnerabilities by building working, safe proof-of-concept exploits in the customer's authorized environment, and it can retest remediated findings on demand.
The homepage reports three results: a first-place ranking on CVE-Bench, an 82.5% reduction in noise compared with competing tools, and 97.5% of highs and criticals fixed. These are the company's own figures and the source does not include methodology or independent verification. Pricing is not published on the homepage. Access begins by contacting the security team to scope an engagement or by requesting a demo. The site says reports are formatted for SOC 2 Type II, ISO 27001, PCI-DSS, and MAS TRM submissions, but acceptance by auditors is the company's own statement.
Key features
- Threat-model-driven AI agents that discover, chain, and exploit vulnerabilities
- Findings validated with safe reproduction traces and proof-of-concept evidence
- Findings mapped to MITRE ATT&CK, OWASP, and NIST CSF
- On-demand retesting of remediated findings
- Testing of web apps, APIs, cloud infrastructure, identity controls, and Active Directory
- Continuous validation of attack paths as code and infrastructure deploy
Best for: Security teams and organizations that want continuous validation of applications, APIs, cloud infrastructure, and AI systems instead of annual point-in-time penetration tests.
Good for
- Each finding is validated with a reproduction trace, according to the site.
- Findings are mapped to MITRE ATT&CK, OWASP, and NIST CSF frameworks.
- Testing runs continuously throughout the year rather than as a single annual assessment.
Watch out for
- Validation is performed in the customer's authorized environment, so testing depends on that authorization.
- Engagements are scoped through the security team or a demo request rather than a self-serve sign-up shown on the homepage.
- Pricing is not stated on the homepage.
FailSafe at a glance
- Website
- getfailsafe.com
- Type
- Website
- Pricing
- Not confirmed. Check the site
- Platforms
- Web
- Open source
- Not stated
- Language
- English
- Last checked
- Oct 6, 2026 · Online when checked
- Listed
- Oct 5, 2026
FailSafe alternatives
Tools and sites you could use instead, ranked by how closely they match.

Hexens audits blockchain systems and offers continuous threat exposure monitoring, alongside research on smart contract platform vulnerabilities.

OtterSec audits blockchain systems, including layer-one networks, wallets, DeFi protocols, bridges, and related infrastructure.

Three Sigma audits blockchain code and DeFi systems, reporting security findings and services for Web3 projects.

Trail of Bits publishes security reviews, research, open-source tools, and talks covering software, blockchains, and AI systems.

Steakhouse Financial builds on-chain stablecoin and yield products, including curated Morpho vaults and white-label platform offerings.
Popular in Portfolio & Security Tools
Well-known listings from the same topic.
CertiKcertik.comDeFiSafetydefisafety.comChainalysischainalysis.comNexus Mutualnexusmutual.iofomofomo.familyKPKkpk.io


FailSafe FAQ
How does SWARM differ from a traditional pentest?
The site describes traditional pentests as point-in-time snapshots conducted once a year. SWARM runs continuously throughout the year and retests remediated findings on demand.
How does FailSafe handle false positives?
According to the site, SWARM builds working, safe proof-of-concept exploits in the authorized environment. A vulnerability that cannot be exploited in context is not reported as an emergency.
What does FailSafe test?
The site lists web applications, APIs, cloud infrastructure, identity controls, Active Directory, LLM applications, AI agents, MCP servers, and specialized critical code.
Is something wrong or out of date?
Tell us and an editor will check it.
Own this website?
Claim this listing
Claim the listing and suggest updates yourself. An editor checks every claim first.