
ClawMoat
ClawMoat helps guard AI agents against data leaks, unsafe tool use, and poisoned dependencies through an open-source firewall.
About ClawMoat
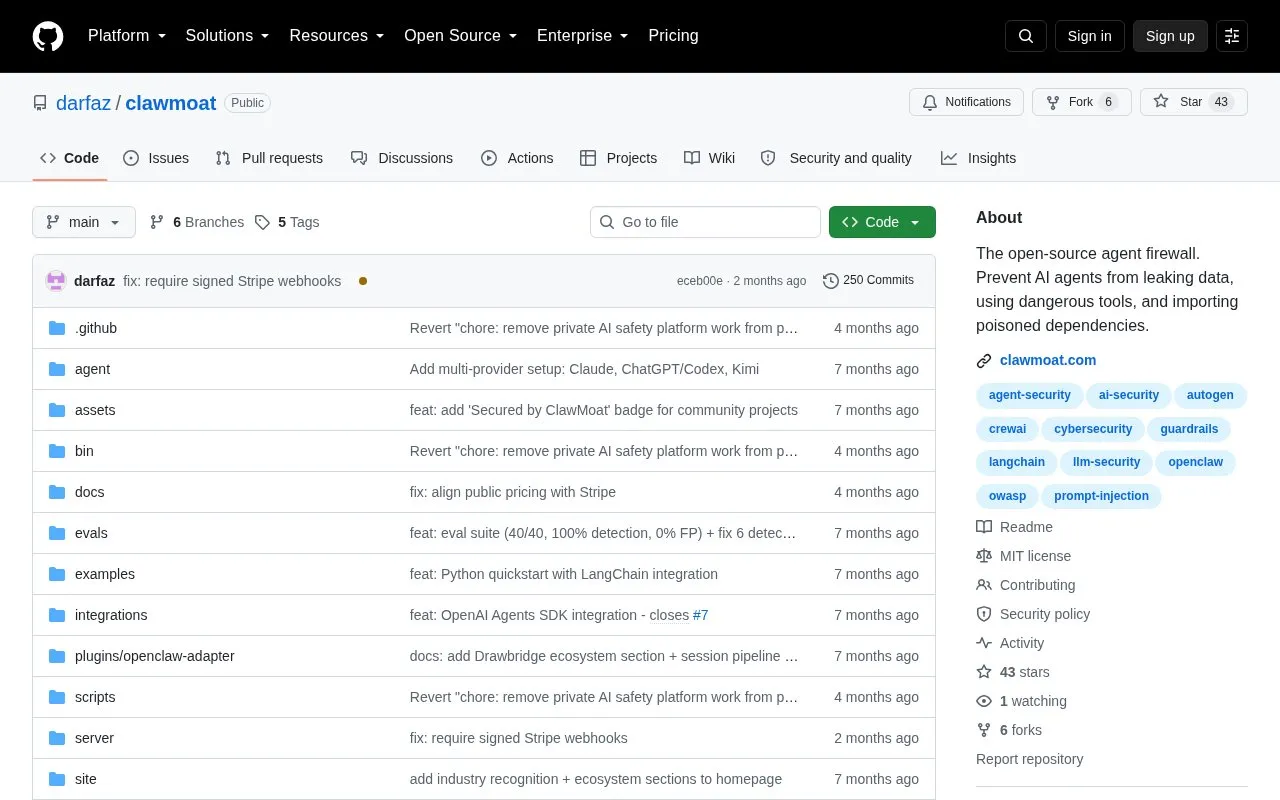
ClawMoat is an open-source runtime security tool for AI agents, described as a firewall that aims to keep agents from leaking data, using dangerous tools, and importing poisoned dependencies. Its homepage describes it as covering desktop agents that have access to files, shell, browser, MCP, cron, and secrets. The repository is published on GitHub under an open-source license, and its files include a threat model and a security policy.
The homepage describes three additional modules. Research Preflight is a command-line control layer for regulated equity research workflows. It checks drafts, transcripts, filings, and model extracts for unsupported claims, missing citations, and other issues, then exports an evidence receipt for supervisor review. Home Network Guard, run through the clawmoat home commands, inventories local devices and flags certain IoT and proxy-related indicators. The homepage lists pricing as unknown, and it does not state which features are available on any plan.
Key features
- Runtime security for agents touching files, shell, browser, MCP, cron, secrets
- Official sanitizer plugin for the OpenClaw security pipeline
- Research Preflight checks for unsupported claims and missing source citations
- Evidence receipt export for supervisor review of research drafts
- Tamper-evident supervision ledger with packet and previous-entry hashes
- Home scan inventories local devices and flags exposed Telnet or ADB
Best for: Developers and security teams running desktop AI agents with access to files, shell, or browser tools, and compliance teams in regulated research workflows.
Good for
- Source code, a threat model, and a security policy are published in the repository.
- Research Preflight records checks in a ledger built on hashes, intended for supervisor review.
- Home watch saves a local baseline file so later scans can be compared against it.
Watch out for
- Proxy-like DNS and outbound behavior are flagged only when logs are provided.
- Signed external anchors are optional and depend on an external storage target such as S3 object lock.
- Research Preflight is described for limited research workflows, not as a general-purpose control.
ClawMoat at a glance
- Website
- github.com/darfaz/clawmoat
- Category
- Privacy & Security › Security Tools
- Type
- Open-source project
- Pricing
- Not confirmed. Check the site
- Open source
- Yes · Source code
- Language
- English
- Last checked
- Oct 6, 2026 · Online when checked
- Listed
- Oct 5, 2026
Guides for Security Tools
ClawMoat alternatives
Tools and sites you could use instead, ranked by how closely they match.

The action firewall for AI agents. Enforce policy and human approval before risky tool calls, shell commands, workflows, and production changes, with auditable evidence.

Karma Firewall is an Android firewall that states it requires no internet permission and intercepts no allowed user traffic.
Open source
24 alternatives
Agentic Radar scans agent workflows for security issues and helps developers review potential risks.
Open source
24 alternatives
Set network rules by application or globally with Fort Firewall for Windows.
Open source
24 alternatives
Manage Android firewall rules with AFWall+, an iptables-based firewall app.
Open source
24 alternatives
This GitHub list curates GPT agents designed for cybersecurity work and related security tasks.
Open source
24 alternativesPopular in Security Tools
Well-known listings from the same topic.
Online Password Hash Crackonlinehashcrack.comOTP Authapps.apple.com/app/otp-auth/id659877384MD5 reverse lookupmd5.gromweb.comMozilla SSLssl-config.mozilla.orgchallenges.rechallenges.reGoPlus Locker V3gopluslabs.io


ClawMoat FAQ
Where does Home Network Guard store its baseline?
Running home watch saves a local baseline in ~/.clawmoat/home-watch-baseline.json, and later scans are compared against it.
Does the research ledger require an external service?
No. Signed external anchors for retained ledger head hashes are optional. The homepage gives S3 object lock as one example of a storage target.
Is something wrong or out of date?
Tell us and an editor will check it.
Own this website?
Claim this listing
Claim the listing and suggest updates yourself. An editor checks every claim first.