
Dockle
Security and best-practice issues in container images can be checked with Dockle.
About Dockle
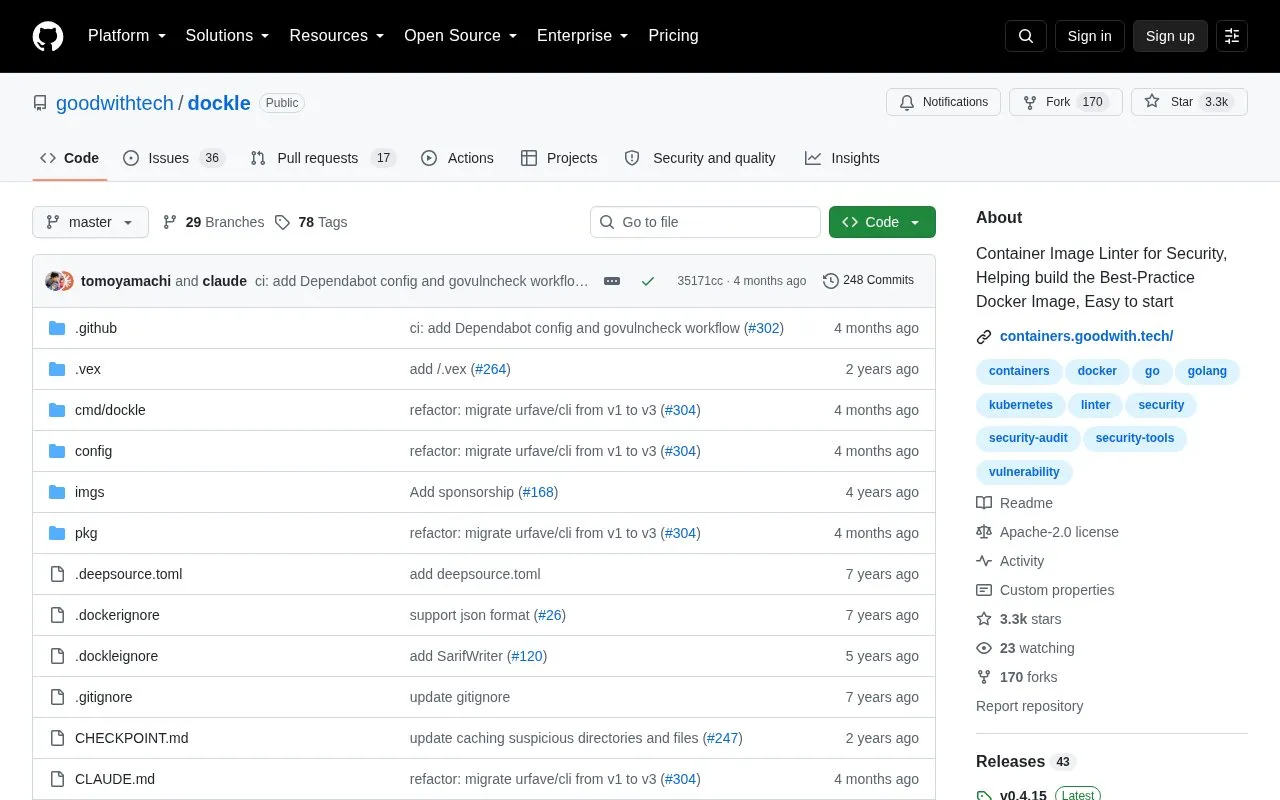
Dockle is an open source container image linter that checks Docker images for security issues and practice checkpoints, including CIS Benchmarks. It can scan a named image or an image file, save results as JSON or SARIF, and adjust scans with exit codes, exit levels, and ignored checkpoints.
Key features
- Scan container image by specifying image name
- Scan saved image file
- Save results as JSON or SARIF
- Set exit code and exit level for scans
- Ignore selected checkpoints
- Accept or reject specified environment variables and files
Best for: People who build or review Docker container images and need security and practice checks.
Good for
- Includes CIS Benchmarks in checkpoints
- Runs as a binary with no dependency listed in comparison
- Described for use with several CI systems
Dockle at a glance
- Category
- Privacy & Security › Security Tools
- Type
- Open-source project
- Pricing
- Not confirmed. Check the site
- Open source
- Yes · Source code
- Language
- English
- Last checked
- Oct 5, 2026 · Online when checked
- Listed
- Oct 5, 2026
Guides for Security Tools
Dockle alternatives
Tools and sites you could use instead, ranked by how closely they match.

Analyze software with Ghidra, a framework for reverse engineering compiled programs.
Open source
24 alternatives
Snyk CLI scans and monitors software projects for security vulnerabilities.

AllSafe provides an intentionally vulnerable Android app for security testing and practice.
Open source
24 alternatives
Agentic Radar scans agent workflows for security issues and helps developers review potential risks.
Open source
24 alternatives
Browse a curated collection of information security tools, links, and learning resources.
Open source
24 alternatives
This GitHub list collects books, guidelines, blogs, videos, tools, and cases related to CI/CD security.
Open source
24 alternativesPopular in Security Tools
Well-known listings from the same topic.
Online Password Hash Crackonlinehashcrack.comOTP Authapps.apple.com/app/otp-auth/id659877384MD5 reverse lookupmd5.gromweb.comMozilla SSLssl-config.mozilla.orgchallenges.rechallenges.reGoPlus Locker V3gopluslabs.io


Dockle FAQ
How do I scan an image?
Run dockle with the image name, for example dockle [YOUR_IMAGE_NAME].
What result formats can be saved?
Results can be saved as JSON or SARIF.
Can it be used in continuous integration?
Use with GitHub Action, Travis CI, CircleCI, GitLab CI, and Jenkins is described.
Is something wrong or out of date?
Tell us and an editor will check it.
Own this website?
Claim this listing
Claim the listing and suggest updates yourself. An editor checks every claim first.