

AIlice provides an autonomous, general-purpose AI agent through its open-source repository.
Open source
24 alternativespiia-engram provides local-first AI memory that users can inspect and edit across coding tools.
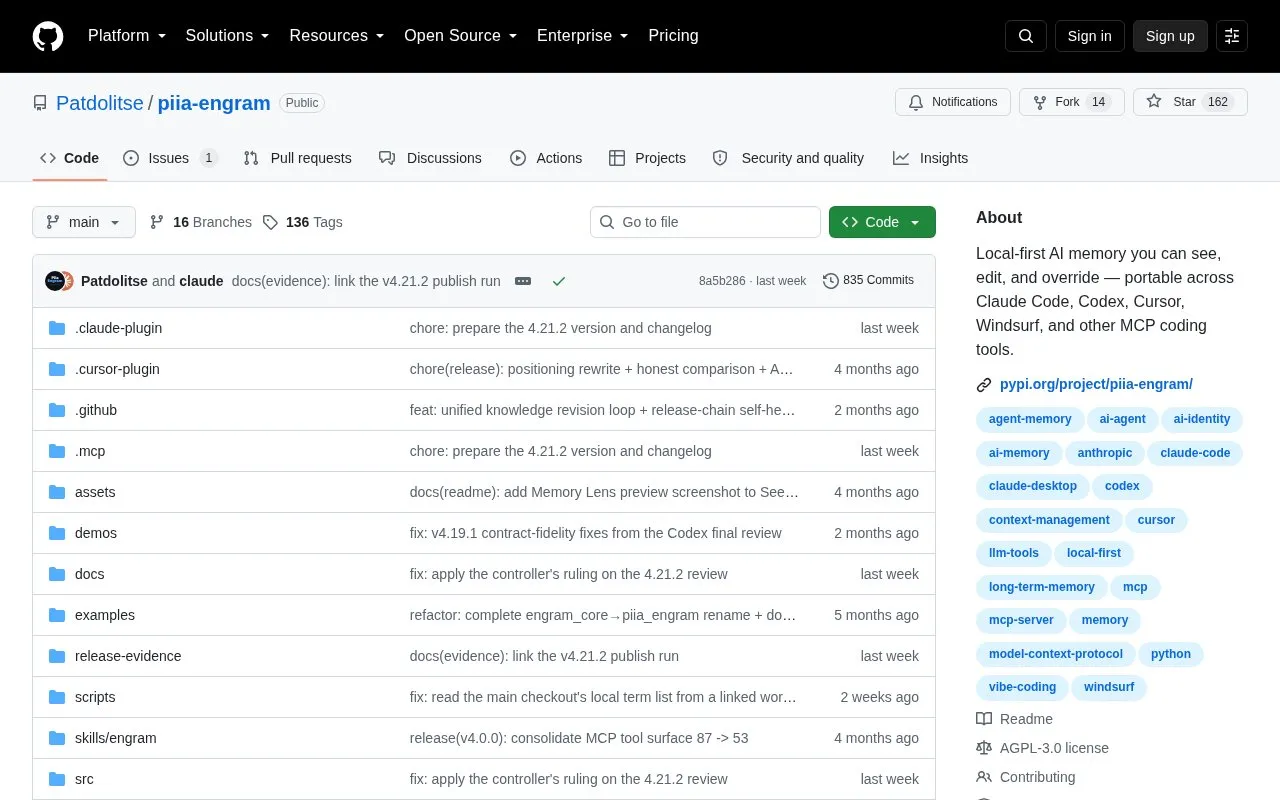
piia-engram is an open-source, local-first personal AI identity layer for MCP-compatible coding tools such as Claude Code, Codex, Cursor, and Windsurf. It stores your preferences, quality standards, lessons learned, decisions, and project context as JSON and Markdown files under ~/.engram/, so several coding agents can start from the same understanding of you. The project describes itself as a user-owned layer above each tool's native memory, not an agent memory database.
AI-proposed writes are governed by an approval policy. High-risk items, including credentials, shell commands, MCP configuration, and permission rules, wait for user review. Low and medium writes are absorbed automatically but remain auditable and reversible. The ENGRAM_APPROVAL=strict setting gates every write. A "verified" item means it was accepted by the user or by the configured policy; it is not re-checked against current code. Session resume output can also include unreviewed checkpoints and snapshots, which do not authorize actions. The core store does not require a cloud account, but the source does not describe every external service that may be involved.
Tools and sites you could use instead, ranked by how closely they match.
AIlice provides an autonomous, general-purpose AI agent through its open-source repository.
XAgent supports autonomous complex task solving with a large language model agent.
AG2 offers open source tools for building and coordinating AI agent systems.
Agent4Rec implements research on generative agents for recommendation systems.
Microsoft’s UFO project focuses on AI agents that work across desktop applications and digital workflows.
An LLM-based autonomous agent controlling real-world applications via RESTful APIs.
Well-known listings from the same topic.
Tell us and an editor will check it.
Claim the listing and suggest updates yourself. An editor checks every claim first.


